Why GDPR-Compliant AI Chatbots Are Essential: Data Privacy & Security in 2026
Why GDPR-Compliant AI Chatbots Are Essential: Data Privacy & Security in 2026
Artificial intelligence has transformed customer engagement and inbound lead generation. Autonomous AI sales agents, website chatbots, and intelligent copilots engage prospects around the clock, answering complex questions and booking meetings in seconds.
However, behind the speed and conversion uplift lies a regulatory reality that no organization can afford to ignore: Data Privacy Regulations (GDPR, CCPA, and the EU AI Act).
Deploying a consumer-grade chatbot or an unvetted large language model (LLM) wrapper on your commercial website can inadvertently expose your organization to regulatory penalties up to €20 million or 4% of annual global turnover under GDPR, alongside severe reputational damage.
In this guide, we break down why GDPR compliance for AI chatbots is not just a legal checkbox, but a foundational requirement for sustainable enterprise growth in 2026.
1. The Collision Between Modern LLMs and Data Protection Laws
Traditional software follows deterministic rules: data goes into designated relational database rows and stays there until updated or deleted. Modern conversational AI, however, introduces dynamic variables:
 Enterprise AI Chatbot Trusted
- Unpredictable User Inputs: Visitors type personally identifiable information (PII)—including names, email addresses, phone numbers, health inquiries, or financial details—directly into chat windows.
- Third-Party Model Leakage: If your chatbot routes raw prompts to public foundation model APIs without zero-retention agreements, that proprietary data may be absorbed or inspected by external providers.
- The "Black Box" Problem: Machine learning models that train indiscriminately cannot simply "forget" a single person's data once embedded in weight matrices.
Under the General Data Protection Regulation (GDPR), European residents (and global visitors interacting with EU-facing companies) are guaranteed clear legal protections. When an AI chatbot operates on your domain, it acts as a data intake mechanism that must adhere strictly to these principles.
2. Key GDPR Principles Every AI Chatbot Must Respect
To maintain continuous regulatory compliance, your AI chatbot deployment must satisfy five fundamental GDPR mandates:
A. Lawful Basis and Explicit Consent (Articles 6 & 7)
Before processing personal data, you must establish a lawful basis—typically legitimate interests or explicit user consent. If the chatbot requests contact information to schedule a demo or send product materials, clear consent notices and links to your Privacy Policy must be accessible prior to submission.
B. Purpose Limitation & Data Minimization (Article 5(1)(c))
Your AI agent must only request and process information strictly necessary for the interaction. For example, if a prospect wants pricing tiers, asking for their physical address or national identification number violates data minimization.
C. Right to Erasure / "Right to be Forgotten" (Article 17)
Users have the legal right to request the deletion of their personal information. If your conversational logs or vector databases store chat transcripts, you must have an automated protocol to purge that specific user's records across all datastores upon verified request.
D. Data Subject Access Requests (DSAR - Article 15)
Under Article 15, prospects can request a full transcript and log of every piece of data your AI collected about them. Your system must maintain structured, searchable logs that can be exported in machine-readable formats.
E. Protection Against Automated Profiling (Article 22)
Article 22 prohibits solely automated decisions that produce legal or similarly significant effects without human oversight. For high-stakes verticals such as legal client intake or healthcare, AI should act as a triaging assistant rather than a unilateral decision-maker.
3. How Modern RAG Architecture Solves the Compliance Paradox
The most secure and compliant way to deploy conversational AI is through Retrieval-Augmented Generation (RAG) coupled with strict multi-tenant database isolation.
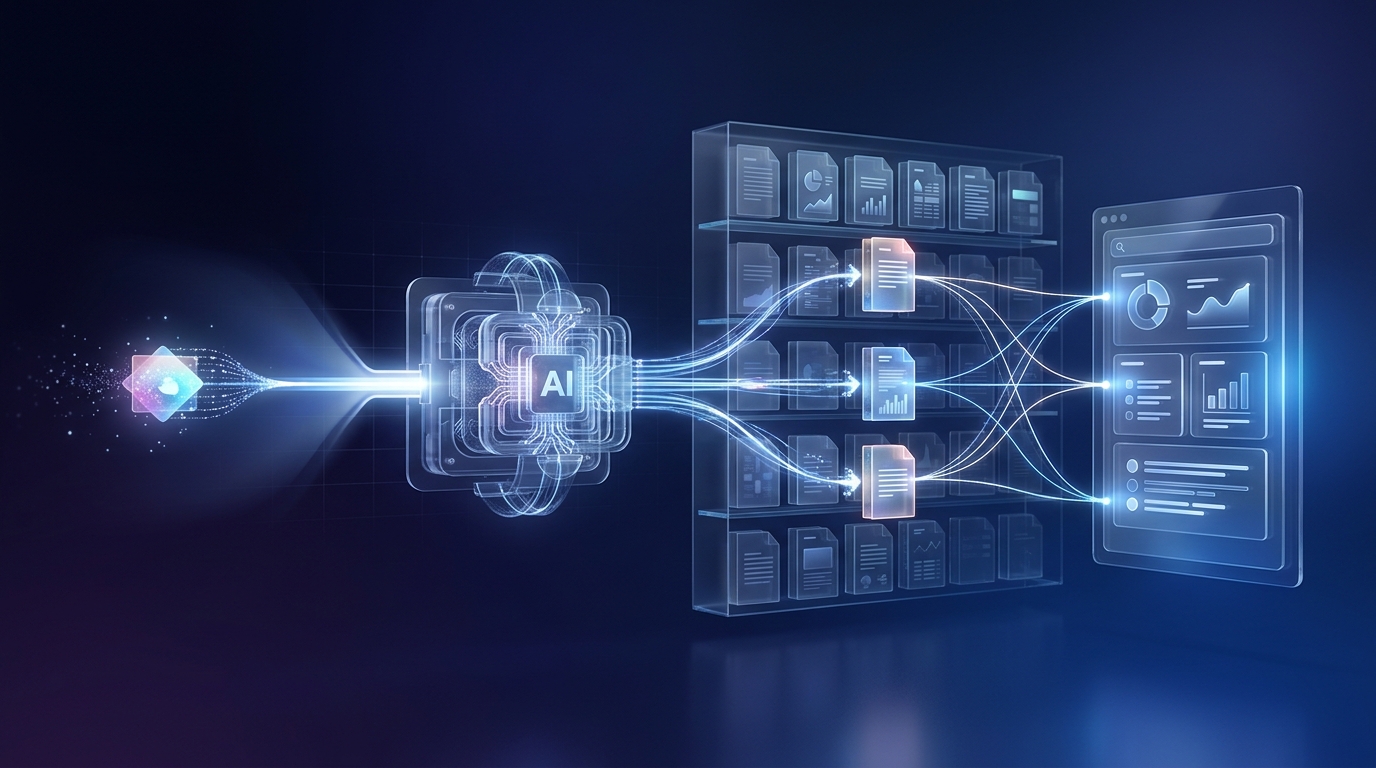 RAG AI Retrieval Process
Rather than allowing an AI to guess answers or hallucinate responses, a RAG-powered engine queries a strictly sandboxed, private vector index containing only verified business collateral (brochures, documentation, pricing sheets).
For a detailed exploration of how this eliminates hallucinations while preserving security, see our deep dive on Solving Hallucinations with RAG.
How LeadAdvisor AI Enforces Enterprise-Grade Security:
- Zero-Training Guarantee: Your visitors' chat transcripts and uploaded company documents are never used to train public or foundational models.
- AES-256 Encryption at Rest: All stored transcripts, vector embeddings, and contact leads are secured using banking-grade AES-256 encryption.
- TLS 1.3 in Transit: All client-to-server communications are encrypted with modern TLS 1.3 cryptographic suites.
- Multi-Tenant Logical Isolation: Each customer's vector database namespace and knowledge base are strictly segregated, preventing cross-tenant data leakage.
- Automated Retention Schedules: Configure custom log retention windows (e.g., 30, 60, or 90 days) after which ephemeral conversational data is automatically purged.
4. The Business Value of Privacy-First AI
Far from being a bottleneck, strict compliance is a competitive differentiator. Enterprise procurement teams, CISOs, and legal counsels now routinely disqualify software vendors that cannot prove GDPR, CCPA, and SOC2 alignment.
| Dimension | Generic Consumer Chatbots | GDPR-Compliant Enterprise AI | | :--- | :--- | :--- | | Data Training | User chats used for model re-training | Strict zero-training policy | | Data Residency | Unspecified global routing | Defined multi-tenant regions | | Encryption | Standard or variable | AES-256 at rest & TLS 1.3 in transit | | Audit Trails | Limited or unindexed | Complete DSAR-ready event logs | | Enterprise Readiness| High legal & compliance risk | Procurement-approved security posture |
When prospects interact with an AI chatbot that transparently discloses its privacy controls, links to its Terms of Service, and respects user rights, trust increases—and higher trust directly translates into higher conversion rates.
5. Deployment Checklist: Is Your AI Chatbot GDPR-Ready?
Before activating any conversational widget on your commercial website, verify this five-point checklist:
- Clear Attribution & Disclosures: Inform visitors that they are communicating with an autonomous AI assistant, with an option to request human handover.
- Accessible Privacy Documentation: Provide direct, one-click access to your Privacy Policy and Terms of Service within or beside the chat widget.
- Data Processing Agreements (DPAs): Ensure your AI vendor signs a comprehensive DPA outlining subprocessor locations, security protocols, and breach notification windows.
- Automated DSAR & Erasure Workflows: Establish an operational mechanism to identify and purge user data upon receipt of a deletion request.
- Private Knowledge Base Isolation: Keep your enterprise documentation strictly partitioned using trained knowledge bases that prevent data mingling.
Secure Your Pipeline with Compliant AI
Scaling pipeline generation should never come at the expense of customer trust or regulatory exposure. By deploying a privacy-first conversational architecture, your business can capture leads 24/7, qualify opportunities automatically, and protect critical enterprise data.
Ready to see how LeadAdvisor AI combines lightning-fast autonomous sales with enterprise data security? Explore our pricing or book a personalized security demo with our team today.